Security basics
What happens after you enter your password in an MFA login?
Your password was accepted, but the website still wants a code. Follow a typical sign-in to see how the password, authenticator code and session fit together.
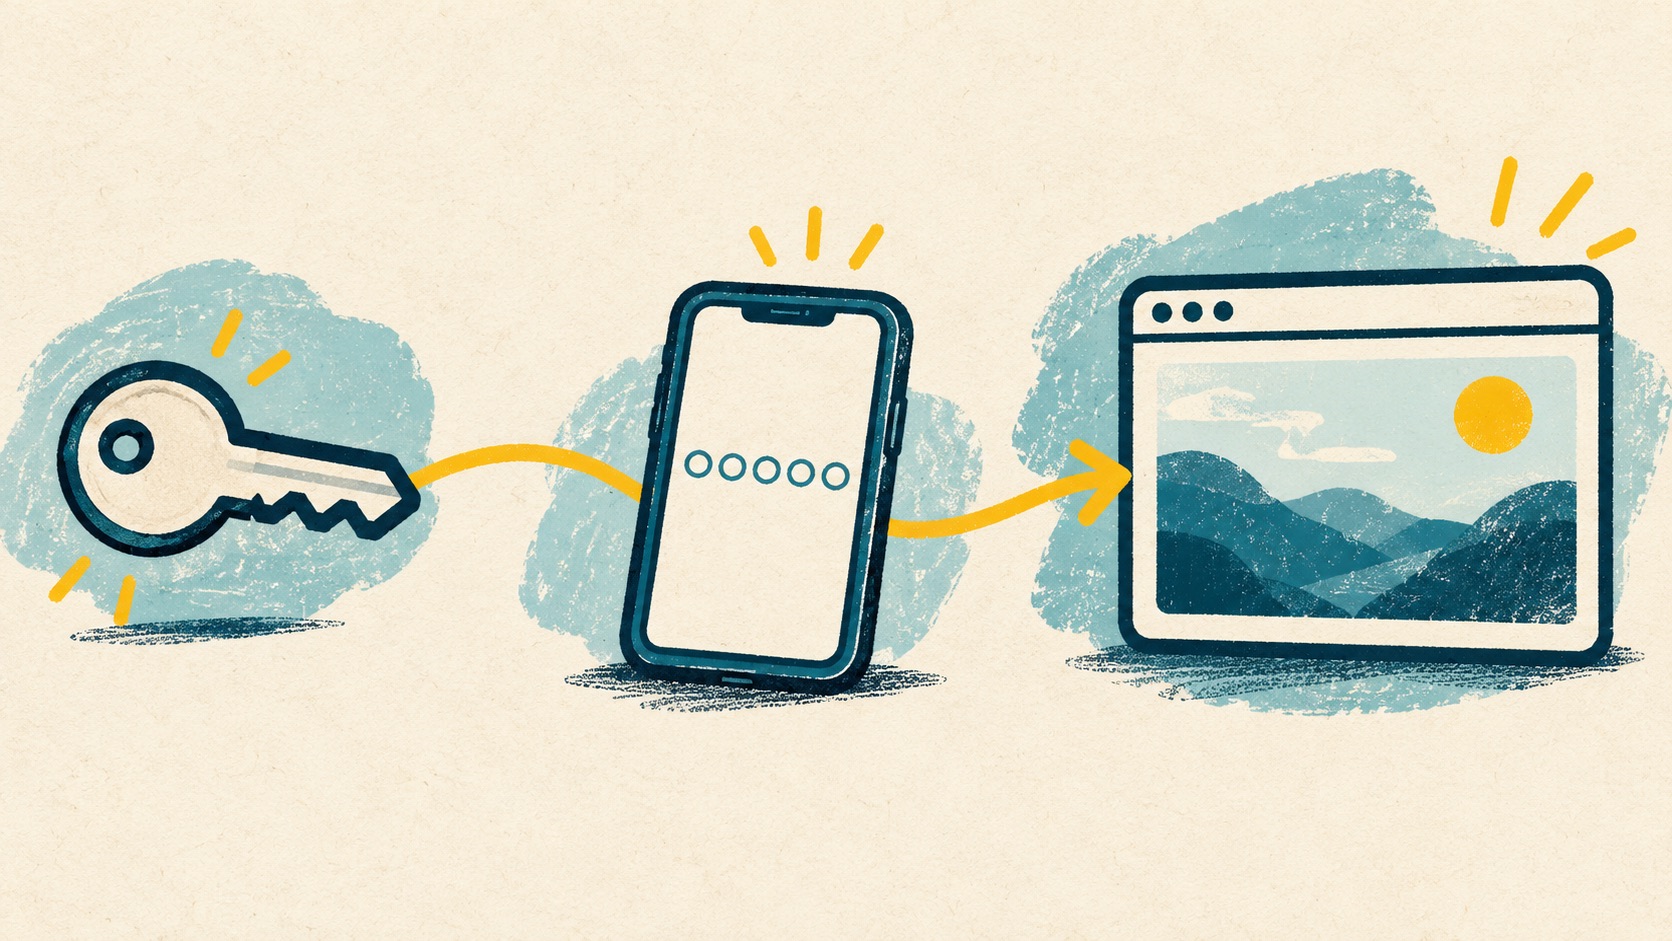
On a website that asks for a password followed by an authenticator code, accepting the password completes only one check. The website then verifies the code you submit. After the required checks, it can establish a session so you can continue using the account.
In this article
Start with the step on your screen
| Screen | Your action | What the website checks |
|---|---|---|
| Account and password | Enter the credentials for this account | The submitted sign-in credentials |
| Authenticator code | Get the current code from the matching entry | The code you submit for verification |
| Signed-in pages | Continue to the account's features | The session accompanying later requests |
A code prompt after your password does not necessarily mean the password failed. Some websites split sign-in into separate checks. This example follows a password-then-code flow; the service you use may arrange its steps differently.
The password and code answer different questions
A password checks knowledge of a secret. A one-time code from an authenticator checks possession of the corresponding credential. If the page is waiting for that code, entering the password again will not finish the step.
Read the field label: does it ask for an authenticator code, an email code or a text message? Similar-looking numbers from different sources are not interchangeable.
The authenticator generates; the website verifies
A TOTP authenticator calculates a code using its saved setup and the current time. The website verifies what you send back. Seeing a changing number on your phone is separate from the website accepting a submission.
In Authenticator Cloud, find the entry for the service and account before taking its current code. If the website rejects it, follow the code troubleshooting steps before starting setup again.
After sign-in, the session takes over
Opening another page usually does not require entering every credential again. One common approach is a session identified by a cookie that the browser sends with later requests. The website checks whether that session is still valid.
A fresh number in your authenticator does not mean you must repeat sign-in every time the code changes. The code belongs to a verification step; the session carries the subsequent visit. The website decides when you need to authenticate again.
Follow the prompt, then check the result
For a sign-in you started, get the code requested by the page. After submitting it, look at the website's response: an account page, another confirmation or an error. This helps locate the step that needs attention.
- Match both the service and account, especially when you have work and personal entries.
- Keep password prompts and different kinds of code prompts separate.
- Use the website's result to confirm completion, not merely the presence of digits in a field.
References
- NIST SP 800-63B: Authenticators and session management
- RFC 6238: TOTP
- MDN: Using HTTP cookies
- OWASP: Authentication Cheat Sheet
See the official guides above for detailed setup instructions.
Use the Authenticator Cloud getting-started guide to add an entry and confirm the first code with the website.